Compliance and high-tech security for fintech companies.
We help you get licensed, meet EU rules and protect your systems. Lawyers and a security IT team under one roof – for fintechs, crypto firms and payment institutions entering the EU via Central Europe.
Audits and licensing without the stress. Paperwork and regulator meetings? Handled.
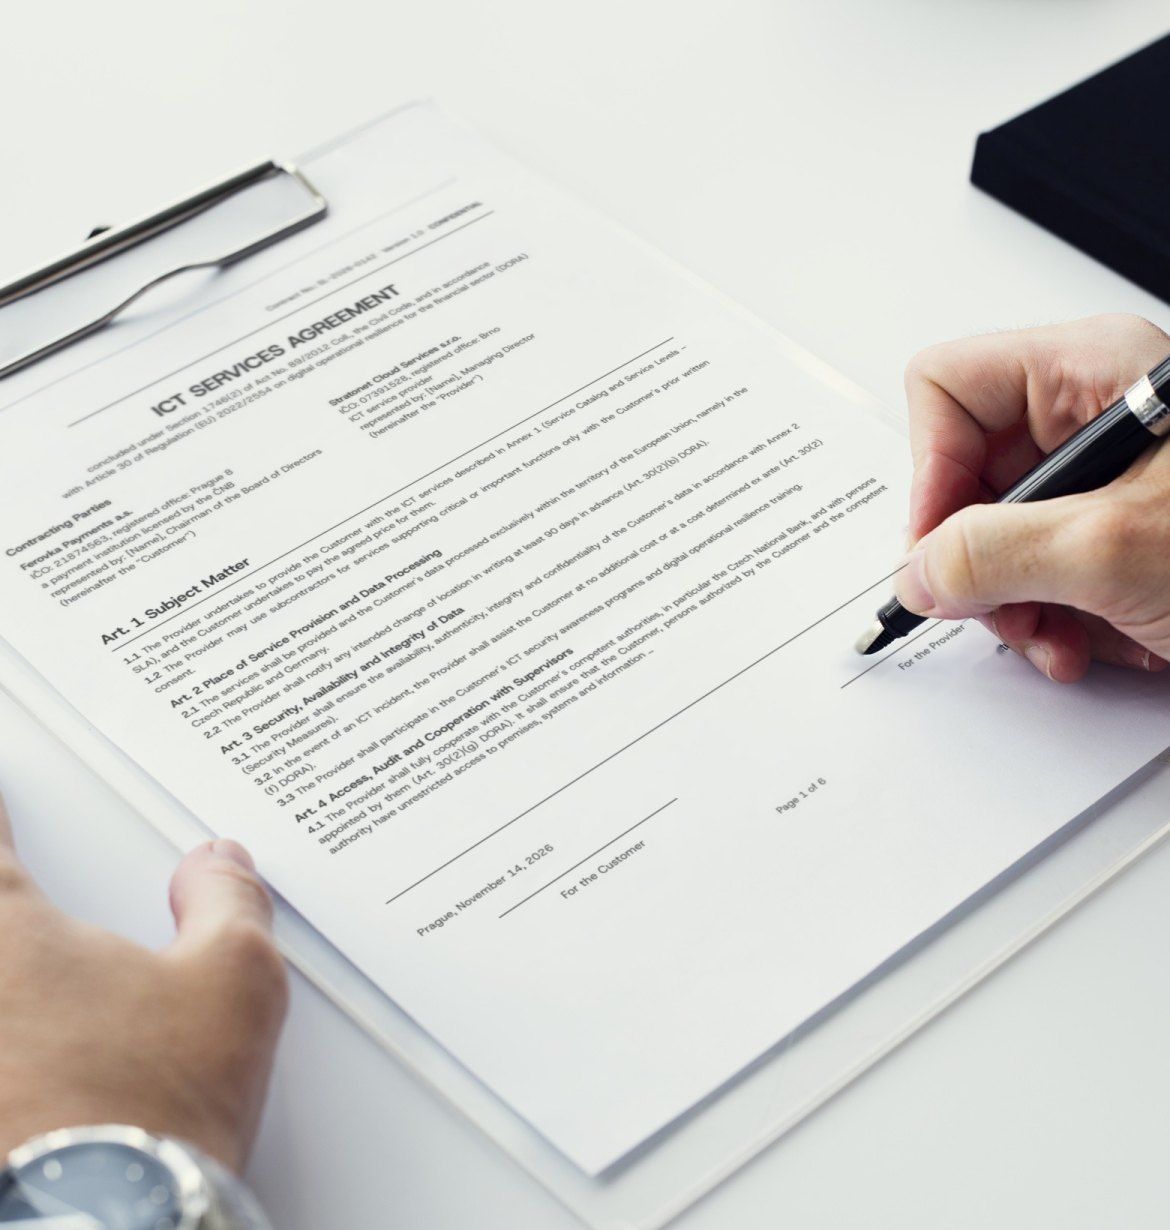
Before the Czech National Bank (ČNB) grants a license or comes to inspect, it wants proof that your policies, contracts and systems are in order. We go through everything with you in advance, fill the gaps and sit beside you at every meeting.
We check where you standContracts, policies, IT – what complies and what doesn't.
We prepare the documentsLicense application, policies, registers and contracts.
We guide you through ČNB meetingsWe answer the regulator's questions and track deadlines.
Consultants write you policies that nobody ever implements in your systems. IT firms deploy tech that doesn't match the regulation. But the regulator wants both – plus proof that the controls actually run.
That's why our documents, implementation and evidence all come from one team.
POLICIESIT DEPLOYMENTEVIDENCE
Consulting firmdocuments, no delivery
IT vendortech, no regulation
Security Labone team, one accountability
Evidence = logs of who accessed your systems and when, tested backup restores and incident records. Exactly what the regulator asks for during an inspection.
17. 1. 2025DORA is in forceYou must prove digital resilience technically, not just on paper.
Mar 31, yearlyRegister of InformationMandatory annual filing to the regulator on all ICT vendors.
2026–2027MiCA in full forceCrypto services only with CASP authorization and ongoing supervision.
24 / 72 hIncident reportingWithout monitoring, you won't report a major incident in time.
Payment approvedCZK 1,249.00 · 0.38 s
Transactions today48 312
Uptime99,98 %
/ 04 TURNKEY FINTECH
From POS terminals to crypto exchanges.
Have an idea for a payment service, app or exchange? We design it, build it, connect it to banks and card networks, and handle the license. You get a finished product that makes money – and is compliant from day one.
Payment gatewayCard payments on the web and in-app
POS and terminalsFrom a single store to a whole branch network
Neobank and walletAccounts, cards and transfers in your own app
Crypto exchange and swapTrading, custody and CASP license
Bank connectivityOpen banking, card schemes and payouts
Licensing, security, operationsČNB, PCI DSS, DORA and 24/7 monitoring
Launching a payment platform or fintech? We take you from license to secure operations.
Not sure what DORA is or which license you need? That's fine. We start with what you want to do – and tell you what the law requires and how to build it technically.
Payment gateways and payment institutions
You accept or send money on behalf of clients.
WE HANDLE LEGAL
ČNB license or registration
Anti-money laundering and client verification rules
−30 %Early client programWe're offering our first three clients a DORA audit at up to 30% off in exchange for a reference and a joint case study.Claim a spot
Licensing and regulation. Handled for you, step by step.
We map your obligations, prepare the documentation and take over communication with the regulator. Your responsible officers get everything “pre-digested.”
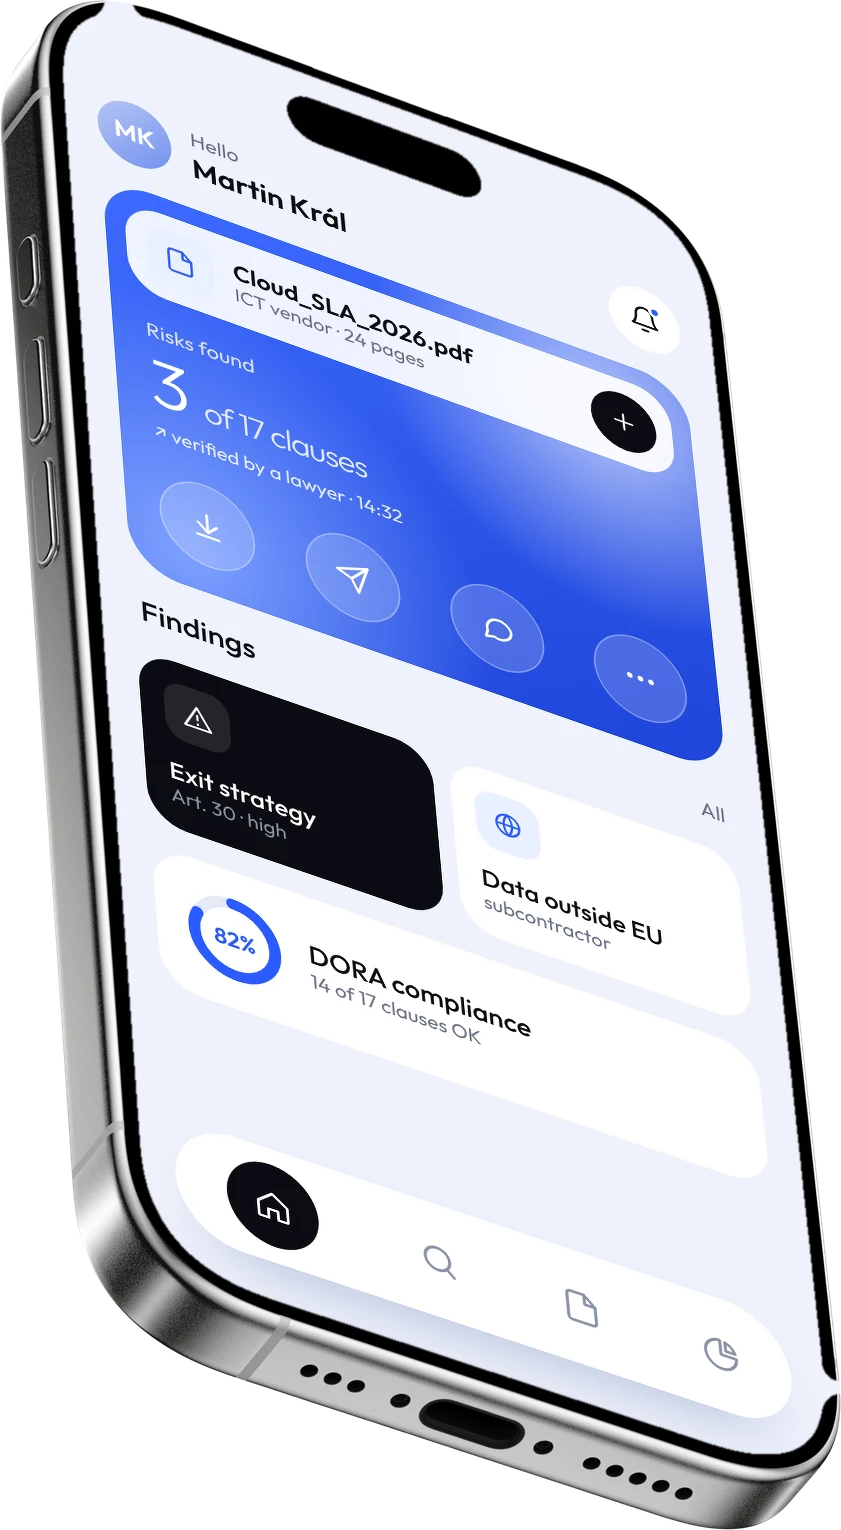
Legal and technical audit in one: we map your ICT contracts, find gaps against Art. 28–30, review your infrastructure and hand over a finished Register of Information.
A security chief and a compliance officer in one team. A monthly retainer instead of two expensive hires.
03
MiCA / CASP package
Crypto service mapping, Art. 62 documentation, capital structure and governance. After authorization, we take over ongoing compliance.
04
Register of Information as a Service
A live dataset instead of a spreadsheet. Automatic xBRL-CSV export and stress-free annual filing.
05
ICT vendor due diligence & AI governance
We vet vendors before you sign and set AI rules in line with the EU AI Act.
/ 09 IT & TECHNICAL DELIVERY
IT that passes inspection. We design it, build it and watch it 24/7.
A policy without technical implementation won't pass any inspection. Our IT team designs, deploys and runs 24/7 the infrastructure your compliance actually rests on.
INFRA
SECURITY
AI & AUTOMATION
COMPLIANCE
Compliance layerpolicies · registers · reporting
AI & automationAPI integrations · xBRL · bots
SecuritySOC · SIEM · IAM · encryption
Infrastructurecloud · on-prem · backups · DR
Backup restore tested
MFA 214 / 214 accounts
Remotely and on-site at your servers.
Compliant cloud & infrastructure
Cloud and on-prem design, migration and operations under DORA and ISO 27001. Data in the EU.
24/7 monitoring (SOC)
We watch your systems around the clock and step in before an attack does damage – even at 3 a.m. on a weekend.
Incident response
Playbooks, forensics and regulator reporting within statutory deadlines.
Penetration testing
A controlled “attack” on demand that finds weak spots before real attackers do.
Access and passwords
Who can access what: two-factor login, account management and a log of every access.
Backups & disaster recovery
We regularly verify that data can be restored and know how fast you'll be back up and running.
Integration & automation
Core-system integration via API and automated reporting with no manual re-keying.
Custom development
KYC/AML modules, internal tools and AI bots built around your exact processes.
AI finds the risks. A lawyer confirms them. You sign.
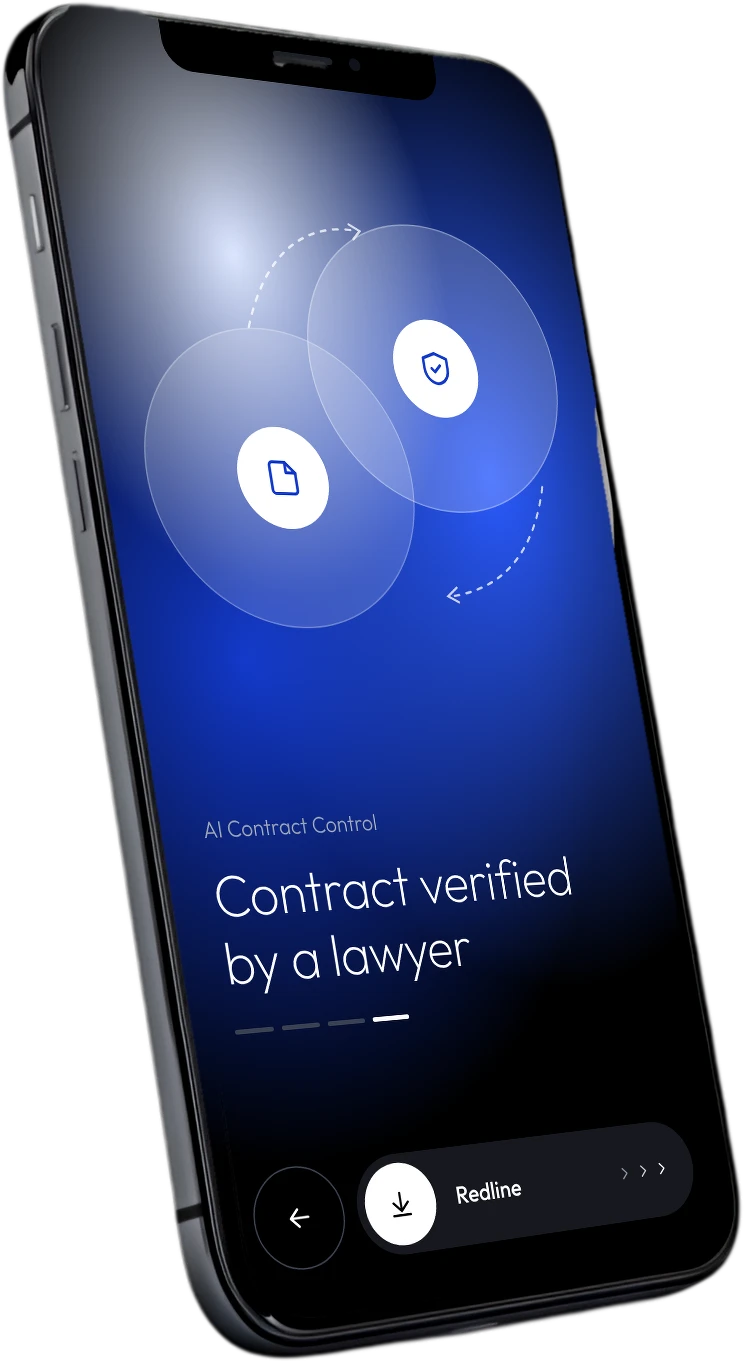
Upload an NDA, supplier, lease or investment agreement. The model extracts the risks and drafts a summary, an experienced lawyer verifies the result – and you get notified straight in Evolio or Telegram.
Human-in-the-loopevery output is checked by a human
/ 11CYBERSECURITY
Attacks won't wait until you're ready. That's why we watch 24/7.
You don't need to understand the tech. Just know that someone watches your systems day and night – and if something happens, they act at once and send you a clear update.
WHAT WE STOP
Encrypted data and ransom demands
An attacker locks your data and demands money. Known as ransomware.
Tested backups – restore operations in hours, not weeks.
Fraudulent emails and invoices
Your accountant gets an “urgent payment order from the CEO.” Known as phishing.
We filter email, train your people and send them practice phishing emails.
Client data leaks
Sensitive data ends up online – and with it, the trust of clients and the regulator.
Encryption and instant alerts on suspicious behavior.
Service outage
Apps or payments stop working and clients leave for competitors.
Failover and a crisis plan: who does what in the first hour.
Compromised access
A stolen password, or a former employee's account nobody closed.
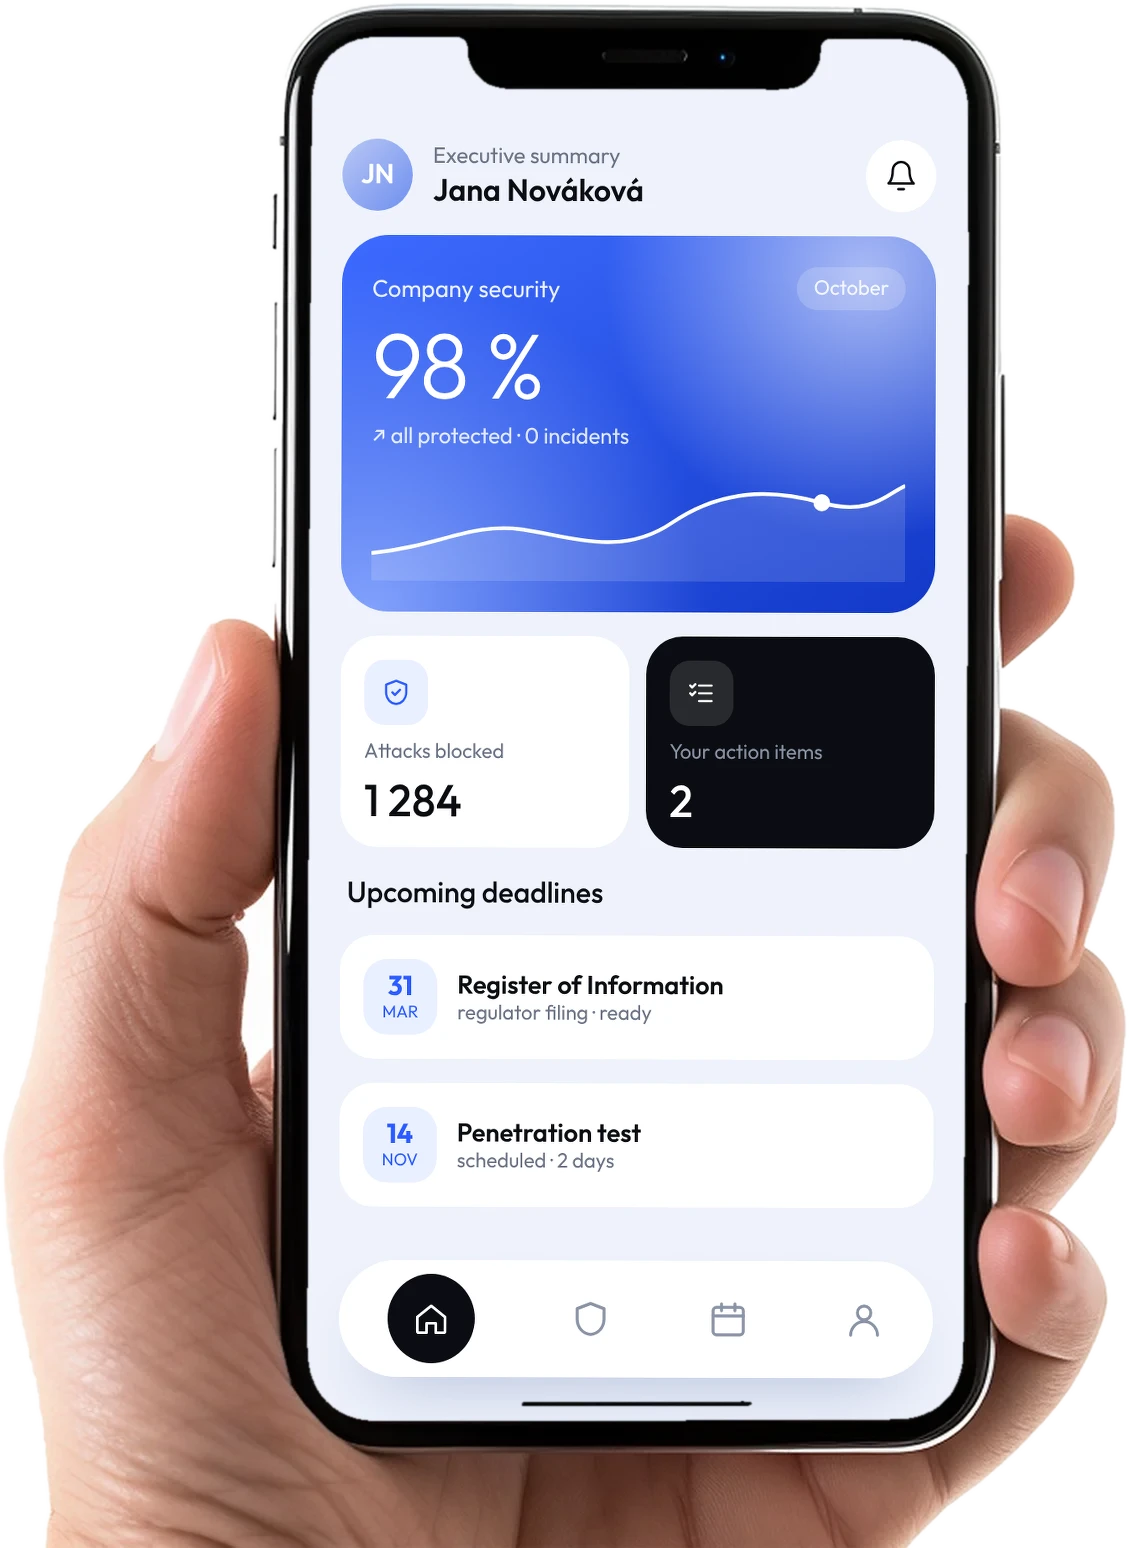
Two-factor login and regular reviews of who has access to what.Executive summary · OctoberPDF
Security statusAll good
Attacks blocked1 284Your action items2
Sample monthly report – no technical jargon.
WHEN SOMETHING HAPPENS
within 15 minutesWe detect suspicious activityAutomation and an on-duty analyst spot something unusual.
within 1 hourWe stop the spreadWe isolate the affected device or account so the damage doesn't grow.
within 24 hoursWe notify the regulatorWe prepare the mandatory DORA or NIS2 report – for you.
within 5 daysWe explain what happenedA report for management and investors: cause, impact, fixes.
No jargon. What the acronyms mean.
For management, investors and anyone who doesn't want to study IT just to know what they're paying for.
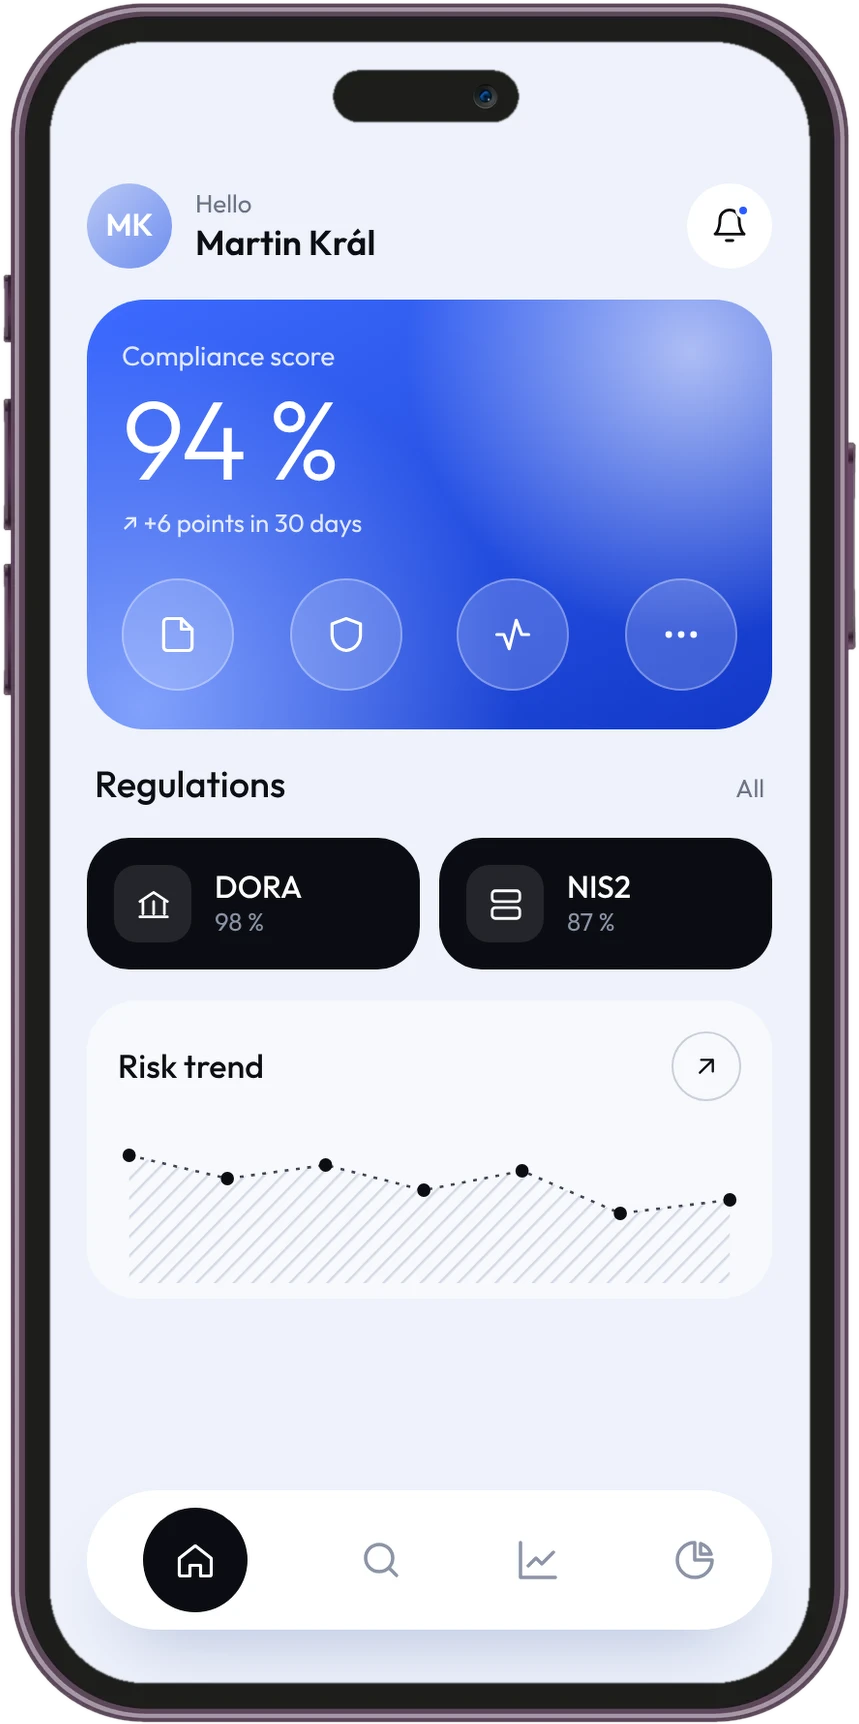
DORAAn EU law requiring financial firms' IT to withstand outages and attacks – and to be able to prove it.
MiCAEU rules for crypto-assets. Anyone doing crypto business needs a license (CASP) and ongoing supervision.
NIS2A cybersecurity law for important companies and their IT vendors.
SOC24/7 security monitoring. A team and tools watching your systems around the clock.
Penetration testA controlled “attack” on demand. We find weak spots before real attackers do.
vCISOA part-time security chief. Executive-level expertise without the cost of a full-time hire.
/ 12 HOW IT WORKS
How we work together. From first meeting to 24/7 monitoring.
No endless “analyses.” Every phase has a clear deliverable, a deadline and a price you know upfront.
01
WEEK 0 · FREE
Consultation
30 minutes. We tell you which regime applies to you and what's most urgent.
Deliverable: priority list by email
02
WEEKS 1–10
Audit
Legal and technical: contracts, processes, infrastructure, access and backups.
Deliverable: gap report + Register of Information
03
WEEKS 11–16
Implementation
We update contracts and policies and deploy the tech: two-factor login, backups, monitoring.
Deliverable: closed gaps + evidence
04
ONGOING
Ops and monitoring
24/7 monitoring, incident reporting within statutory deadlines, annual register filing.
Deliverable: monthly management report
BUILT
FOR THE REGULATED
WORLDData and ops in the EU
Don't see your question?Write to us. We reply within 24 hours – on weekdays, usually the same day.Ask a question
Does DORA, NIS2 or MiCA apply to us?
It depends on your license type and the services you provide – and whether you supply ICT services to financial entities. In a free 30-minute consultation, we'll tell you which regime applies, what type of entity you are and what that means for you.
We're a small company. Are we really a target?
Yes. Attackers often go after smaller financial firms – they handle money and tend to have weaker defenses. Most attacks are automated and don't pick targets by size.
Are you a law firm, consultants or an IT company?
We're a compliance and IT partner: we deliver both the regulatory work and the technical implementation ourselves, and we take responsibility for it. We're not a law firm – if you need legal services in the strict sense, we'll tell you and recommend next steps.
We have policies and ISO 27001. Start from zero?
No. We build on what works and only fill the gaps. ISO 27001 is a good foundation for DORA but covers only part of the requirements – typically missing are the ICT vendor register, contract clauses and resilience testing.
Is paperwork enough for the regulator?
No. During an inspection, the regulator wants to see that protection actually works: logs of who accessed systems and when, tested backup restores and incident records. That's why we deliver the tech too and collect evidence continuously, not a week before the inspection.
Do we need an in-house CISO and compliance officer?
Not necessarily. Virtual roles cover the obligations for a fraction of the cost of two senior hires. As you grow, we'll help you hire an in-house team and hand over the work smoothly.
How fast can you start?
We can usually hold the consultation within a week; the audit starts within [X] weeks of signing and takes 8–16 weeks depending on scope. If a register filing deadline is looming, tell us right away.
Where is our data, and does AI see our contracts?
Data stays in the EU, on infrastructure segregated from other clients. We never use your contracts to train models, and a human reviews every AI output before it reaches you.
You're a new company. Why trust you without references?
The company is backed by founders with 14 years of experience and our own IT infrastructure. We'll sign an NDA before the first meeting, show you anonymized deliverables, and offer our first clients preferential terms in exchange for a reference.
/ 14 LET'S START
Let's find out where you stand. In 30 minutes, for free.
We'll tell you which rules apply to you, what's most urgent and what a solution will cost. No strings attached.